Innovation, Quantum-AI Technology & Law

Blog over Kunstmatige Intelligentie, Quantum, Deep Learning, Blockchain en Big Data Law

Blog over juridische, sociale, ethische en policy aspecten van Kunstmatige Intelligentie, Quantum Computing, Sensing & Communication, Augmented Reality en Robotica, Big Data Wetgeving en Machine Learning Regelgeving. Kennisartikelen inzake de EU AI Act, de Data Governance Act, cloud computing, algoritmes, privacy, virtual reality, blockchain, robotlaw, smart contracts, informatierecht, ICT contracten, online platforms, apps en tools. Europese regels, auteursrecht, chipsrecht, databankrechten en juridische diensten AI recht.

Berichten in Intellectual Property
Quantum Computational Antitrust: How Quantum Computing Could Reshape Competition Enforcement

Antitrust enforcement is becoming a contest between models. Agencies screen procurement databases with algorithms, firms price with reinforcement learning, and scholars at Stanford's CodeX center have organized the discipline of computational antitrust around a simple premise: enforcement must compute as well as the markets it polices. This analysis asks what happens when the computation itself turns quantum.

Why enforcers and firms already compete with algorithms

Brazil's CADE mines bidding data for cartel fingerprints, Korea scores tenders for collusion risk, and the OECD catalogues the tooling. Experiments meanwhile show that independent AI pricing agents can learn supra-competitive strategies without ever communicating, a form of algorithmic collusion that slips past cartel law's agreement requirement. The enforcement arms race is already running on classical hardware, and the stakes were spelled out early in the Oxford JIPLP work on quantum computing, intellectual property and market power.

What quantum computing could add to merger review and cartel screening

Quantum computers will not "try everything at once." Future fault-tolerant machines may improve particular simulation, optimization, and sampling tasks that merger review poses, although no general enforcement advantage has been demonstrated. None of this is deployed at any agency today, and the essay says so plainly. The nearer-term disruption runs through evidence. Harvest-now-decrypt-later means lawfully seized encrypted cartel archives may become readable mid-investigation once quantum machines can run Shor's algorithm, a rare case of the quantum threat working for enforcers, within hard due-process limits.

Why access to quantum computing becomes a competition question

The deepest question is asymmetry. If quantum forecasting and optimization arrive first at firms that already dominate cloud platforms and patent portfolios, informational advantage compounds into entrenched market power through purely unilateral conduct, with no cartel required. Quantum technology therefore poses competition authorities an access question before it poses an evidence question, and the answers will be set by whoever engages first: standards bodies, cloud gatekeepers, or regulators.

The full analysis sets out a five-part readiness agenda for enforcement agencies this decade, from cryptographic inventories of their own case files and leniency archives to sandboxed pilots of quantum screening tools with pre-registered validation protocols. Read it to see how competition agencies can prepare validation protocols, access safeguards, and scoped pilots before quantum-assisted evidence reaches proceedings.

Meer lezen
Northwestern University Debaters Took Up Mauritz Kop's Article on AI, Intellectual Property and the Public Domain (2020)

What happens when a law review article becomes debate material? At Northwestern University in 2020, debaters took up Mauritz Kop's argument that autonomously machine-made works belong in an articulated public domain, and found that the question of who owns AI output divides a room like few others.

The motion: no one should own works made without human creative input

Kop's 2020 article in the Texas Intellectual Property Law Journal stakes out a clear position: when artificial intelligence generates works without meaningful human creative input, no one should own them. The law should avoid stretching authorship to cover such output and should route it into a commons by design, Res Publicae ex Machina, public property from the machine.

The proposition invites adversarial testing. Affirm it, and you must explain to investors why their generative AI pipelines produce unownable output. Oppose it, and you must explain what authorship means when nobody authored anything, and why locking up machine output serves the human creators copyright was invented for.

How the 2020 thought experiment became today's docket

Courts and copyright offices in several jurisdictions have addressed whether works involving generative AI contain enough human authorship for protection, while training data disputes ask the mirror-image question of what machines may learn from. The article's companion doctrine traveled too: the follow-up analysis appeared in a transatlantic volume, as covered in Public Property from the Machine published in Harmonizing Intellectual Property Law for a Trans-Atlantic Knowledge Economy.

That trajectory, from journal article to book chapter to debate material and live litigation theme, is what scholarly impact looks like in practice: arguments that other people find worth having. When students choose to attack and defend a thesis in structured debate, the ideas have left the journal and started doing work in the world.

Why debaters chose this article

Good debate material needs a position clear enough to attack and deep enough to survive the attack. The articulated-public-domain thesis offers both, because it rests on first principles: incentive theory, cultural diversity, the economics of exclusive rights, and the public's stake in what machines make. The full announcement traces the argument, links the article itself, and explains why this AI and IP debate has only sharpened since it was written.

Meer lezen
Harvard–Smithsonian's NASA Astrophysics Data System Indexes the Quantum Nexus Article by Mauritz Kop

Which record Harvard–Smithsonian created for the Nexus Article, and what a bibcode changes

The NASA Astrophysics Data System, run by the Center for Astrophysics | Harvard & Smithsonian under a NASA grant, now holds a permanent record for the book-length article The Nexus of Quantum Technology, Intellectual Property, and National Security: Deterrence by Denial for Democratic Resilience: An LSI Test for Securing the Quantum Industrial Commons, written by Mauritz Kop (Founder of the Stanford Center for Responsible Quantum Technology). The article examines how democratic nations can protect critical quantum infrastructure through a middle path between total closure and open laissez-faire. The record carries the bibcode 2026arXiv260215051K, reproduces the full abstract, names Kop as sole author, dates the work to February 2026, and files the Article under Physics and Society, History and Philosophy of Physics, and Quantum Physics. The document type is recorded as an eprint, the accurate description of a work posted as a preprint on 11 February 2026.

Why a physics catalogue matters for an Article about export controls, and what Kop advises the Pentagon on

Quantum governance scholarship is written by legal and policy scholars and read by physicists, engineers and procurement officers, who search from the other side of the divide. The LSI test — least-trade-restrictive, security-sufficient, innovation-preserving — was built to be applied by the people who draft export-control lists and standards documents, and the Article's claim that the United States and its allies should pursue security-sufficient openness now surfaces in the same results as the technical literature on the capabilities it governs. The index already held nine other works by the same author, among them Nature Physics, Science, Quantum Science and Technology, EPJ Quantum Technology and Physics World. Since August 2026 Kop has served as Quantum Strategy Advisor to the Pentagon, the Office of the Secretary of Defense for Policy, invited to advise on Quantum First across dual-use technology, industrial policy, national and economic security, governance and grand strategy. The role is advisory, carries no employment relationship, and implies no institutional endorsement. The paradigms it carries forward are the Stanford RQT ones: the Ten Principles, the War on the Rocks migration discipline, and the LSI test itself.

Meer lezen
Quantum Nexus LSI Test Published by Vanderbilt JET Law

Most technology law arrives too late: the architecture ships, the market consolidates, and legislators are left regulating what already exists. A new essay in Vanderbilt's Journal of Entertainment & Technology Law argues that quantum technology presents the opposite—and far rarer—situation, and explains what the law should do with it. Quantum law is being written before quantum technology has fully arrived, and that timing is not a defect to apologize for but an opportunity to seize.

A test with three prongs

At the center of the essay stands the LSI test, a doctrinal instrument for dual-use governance that asks of every state intervention whether it is the least trade-restrictive, security-sufficient, and innovation-preserving measure available. The shift in emphasis is subtle but consequential: the question is no longer whether a government possesses a restrictive tool—export control, outbound investment screening, patent secrecy—but whether it is deploying the narrowest one that actually works. Between the romantics of total openness and the reflexes of total restriction, the test stakes out a defensible middle ground the essay calls security-sufficient openness.

Patents and export controls, one system

The essay's second contribution is diagnostic. Intellectual property and national security are conventionally treated as separate fields with separate experts and separate statutes. In quantum practice they behave as one entangled legal control plane: a single patent disclosure can simultaneously raise eligibility questions under Alice, research-security questions under the export-control regime, and commercialization questions under Bayh-Dole and the federal acquisition rules. Reading them together is not an academic nicety—it is the only way to see where over-securitization would quietly strangle the startups, standards participation, and allied interoperability on which democratic quantum leadership depends, a dynamic explored across the MINDS quantum strategy research at CIGI.

From a six-paragraph essay to a coalition playbook

Behind the essay stands the full Quantum Nexus Article—a book-length treatment on arXiv that develops the LSI test into an implementable coalition playbook: empirically anchored criteria, differentiated guardrails with red-zone domains where denial is the default, and secure closed-loop enclaves for high-sensitivity collaborative research. The stakes are framed without euphemism: U.S. assessments now call for a Quantum First posture by 2030, China's program advances under military-civil fusion, and the choice before democratic legislators is whether the coming wall of quantum regulation will be disciplined by doctrine or improvised under pressure. For lawyers, the essay is a preview of their next decade; for policymakers, it is a usable standard; and for the quantum community, it is an argument that the rules now being written deserve the same precision as the systems they will govern.

Meer lezen
Mauritz Kop Principal Investigator of MINDS Quantum Strategy Grant at CIGI

Waterloo, February 18, 2026—The Centre for International Governance Innovation (CIGI) has awarded Mauritz Kop a new leadership role as Principal Investigator (incoming) of a MINDS Targeted Engagement Grant on Quantum Strategy. The grant advances a central proposition of his recent work: quantum technologies are no longer best understood as a narrow scientific frontier or a conventional innovation file. They have become a strategic domain in which law, industrial policy, intellectual property, defense planning, and geopolitical competition now converge.

That convergence matters because quantum capability is being built in an era of systemic rivalry, supply-chain vulnerability, and technological coercion. In that environment, democratic states cannot afford to treat quantum merely as a research ecosystem problem. They must govern it as part of a broader strategy for safeguarding the democratic industrial commons: the shared base of talent, infrastructure, know-how, trusted supply chains, standards, and institutions on which long-run security, prosperity, and coalition advantage depend.

What MINDS in Defence and Security Is and Why This Grant Fits

The MINDS program—Mobilizing Insights in Defence and Security—is a Canadian Department of National Defence initiative designed to strengthen evidence-based defense policy thinking and foster the next generation of defense and security experts. Its Targeted Engagement Grants provide non-recurring support for projects such as workshops, roundtables, research, and publications, and they are assessed primarily against the annual Defence Policy Challenges.

The current 2025-2026 MINDS challenge set is especially well aligned with the subject matter of this grant. The official challenge framework emphasizes several critical priorities: securing Canada’s sovereignty and continental defense posture; attracting advanced-technology talent across the defense sector; and strengthening the defense industrial base through resilient supply chains and dual-use technologies such as quantum and artificial intelligence. Furthermore, the framework addresses the pressures of strategic competition—including adversarial exploitation of vulnerabilities—and the accelerating adoption of pan-domain, emerging technologies where interoperability, trust, and responsible governance must be preserved.

Strategic Leadership and Human Capital

Kop’s fellowship at CIGI has centered on the governance of transformative technologies, especially quantum technology, AI, dual-use export controls, national security, and intellectual property. The new grant builds directly on that portfolio, but with a more operational mandate. As incoming Principal Investigator, his role will be to provide the project’s strategic and intellectual leadership: conceptualizing the workshop, defining the central themes and policy questions, structuring the panels for direct relevance to Canadian defense audiences, chairing the main event, moderating key expert sessions, identifying high-level contributors, and guiding the project’s analytical outputs.

The Quantum Nexus Paper Behind the Grant

The grant builds on Kop’s recent paper, The Nexus of Quantum Technology, Intellectual Property, and National Security: An LSI Test for Securing the Quantum Industrial Commons, now available on arXiv.

In that paper, he argues that quantum technologies have moved from laboratory structures to the geopolitical stage, and that democratic states therefore need a governance model that is neither naively open nor reflexively protectionist. The paper's contribution is an implementable coalition playbook, offering empirically anchored criteria, templates, and differentiated guardrails - including red zone domains where denial is the default - to avoid both over-securitization and under-securitization. Properly applied, LSI reduces the risk of a self-defeating hard decoupling from China while establishing standards-first interoperability as a stabilizing eigenstate of the international order and enabling RQT by design to shape trusted adoption pathways beyond the coalition, including in the majority world.

Meer lezen
An LSI Test for Securing the Quantum Industrial Commons

Mauritz Kop—Founder of the Stanford Center for Responsible Quantum Technology and a CIGI Senior Fellow—has posted as a preprint a book-length Article that reframes quantum strategy as a problem of disciplined openness. The Nexus of Quantum Technology, Intellectual Property, and National Security argues that democracies should pursue neither closure nor laissez-faire, but "security-sufficient openness," screened through a single administrable test. It is a strategic companion to the cryptographic argument set out in "A Bletchley Park for the Quantum Age."

Deterrence by denial for democratic resilience

The Article's organizing idea is responsible quantum technology reframed as values-based deterrence by denial: a legal, ethical, and institutional control plane that protects the shared "quantum industrial commons"—talent, tooling, standards, supply chains, and the research base—against authoritarian appropriation. Deterrence by denial aims to make hostile gains too slow or costly to be worthwhile, rather than relying on the threat of retaliation, and the Article presents it as the least escalatory way to preserve crisis stability. It situates the analysis against an approaching strategic "event horizon," citing the U.S.-China Economic and Security Review Commission's call for a "Quantum First by 2030" posture and parallel White House initiatives to secure critical inputs.

The LSI test

The central contribution is the LSI test, which asks whether any given control is least-trade-restrictive, security-sufficient, and innovation-preserving. The test is built to avoid two failure modes: over-securitization, which chills publication, standards leadership, and venture formation, and under-securitization, which leaks crown-jewel capabilities that are slow to reacquire. LSI is applied across a "pillarized" quantum stack—computing, sensing, simulation, networking, communication, quantum-AI hybrids, and enabling materials—and to its upstream dependencies in patent and trade-secret doctrine, government-funded IP and data rights, export controls, investment screening, and cryptographic baselines including post-quantum cryptography and crypto-agility. The framing borrows from physics with care: because the relevant systems are genuinely probabilistic, the Article uses the "Eight Worlds" scenario method to keep governance robust across divergent futures.

A coalition playbook against a "Silicon Curtain"

Rather than stop at theory, the Article assembles an implementable coalition playbook—administrable criteria, templates, and differentiated guardrails, including red-zone domains where denial is the default—and integrates instruments of economic statecraft such as a strategic critical-minerals reserve and a Quantum Criticality Index. Its closing warning is that mishandled securitization could raise a self-defeating "Silicon Curtain" between allied innovators; the constructive alternative is standards-first interoperability treated as a stabilizing feature of the international order. The work has been posted as a preprint on arXiv and is announced on AIRecht in the Nexus paper announcement.

Meer lezen
The Nexus of Quantum Technology, Intellectual Property, and National Security

Some moments in technology policy demand a text that turns scattered anxieties into administrable law. For the collision of quantum technology, intellectual property, and national security, Mauritz Kop's book-length Article on arXiv makes that move: The Nexus of Quantum Technology, Intellectual Property, and National Security: An LSI Test for Securing the Quantum Industrial Commons—a work that reads today's probabilistic security environment like a wavefunction of plausible futures, and asks which policy choices will collapse it into an outcome democracies can live with.

The claim: security-sufficient openness

The Article's central claim is that the United States and its allies should pursue security-sufficient openness, operationalized through an LSI test: every intervention—an export control, an outbound-investment screen, a patent-secrecy order—must be the least trade-restrictive, security-sufficient, innovation-preserving measure available, whether the actor is a state or a private firm. Between total openness, which hands strategic capabilities to rivals mobilized under military-civil fusion, and total restriction, which strangles the science, the test stakes out the only ground that is defensible in both senses of the word.

Red zones, enclaves, and economic statecraft

What makes the work more than a framework essay is its machinery. The Article delivers an implementable coalition playbook: empirically anchored criteria, templates, and differentiated guardrails—including red-zone domains where denial is the default—plus secure closed-loop enclaves where allied researchers can pursue high-sensitivity R&D without choosing between secrecy and collaboration. The instruments of economic statecraft that democracies have increasingly been deploying are integrated here into a single disciplined doctrine, with the U.S. assessments calling for a Quantum First posture by 2030 supplying the deadline.

What is at stake

The Article names the twin failure modes precisely. Over-securitize, and democracies erect a self-defeating Silicon Curtain—suppressing publication, standards participation, and startup formation until the alliance walls itself off from its own innovation. Under-securitize, and strategically meaningful capabilities in computing, sensing, and cryptanalysis diffuse to adversaries faster than open societies can respond. Threading that needle is the geostrategic design problem of the decade—the same problem Kop works on as an expert at the Eric Schmidt-backed von Neumann Commission on quantum-AI geostrategy. Properly applied, the LSI test secures the quantum industrial commons without suffocating the scientific commons beneath it—and extends trusted adoption pathways to the majority world. This post walks through the Article's argument, its playbook, and what both mean for the lawyers and legislators who will write the quantum statutes of the late 2020s.

Meer lezen
CIGI Publishes Global Quantum Policy Brief by Mauritz Kop and Tracey Forrest

Waterloo, 5 February 2026—The Centre for International Governance Innovation (CIGI) has published a new policy brief, Global Quantum Governance: From Principles to Practice, authored by Mauritz Kop and Tracey Forrest. The brief is written for policy makers, regulators, standards bodies, and industry actors facing a practical transition: quantum technologies are moving from laboratory milestones toward deployment pathways where governance choices—especially around cybersecurity and cross-border infrastructure—become difficult to reverse.

Download the Policy Brief here: https://www.cigionline.org/documents/3746/PB_No.222_Kop_and_Forrest.pdf

Why this brief on quantum governance, and why now

The brief’s central timing claim is that near-term milestones—particularly post-quantum cryptography (PQC) migration and quantum networking—create a governance tipping point. After that point, certain security and societal harms may be costly (or impossible) to remediate. In the brief’s framing, PQC migration is not merely an engineering update; it is a “temporal rights and resilience” imperative because present-day decisions about crypto-agility, key life-cycle management, and data minimization determine whether sensitive data remains protected against future adversaries.

This urgency is paired with a structural diagnosis: national initiatives—including the EU’s proposed Quantum Act—are important, but insufficient on their own given quantum’s dual-use characteristics, global supply chains, and asymmetric capabilities across states and firms. The authors argue for a governance architecture that is “standards-first” and internationally coordinated, capable of sustaining what they call “security-sufficient openness,” and overseen by an International Quantum Agency.

The brief’s recommendations in practical terms

The brief concludes with a multi-pronged path “from principles to practice,” emphasizing four implementable priorities:

  1. Strengthen foundations through standards and PQC execution: align cryptographic profiles across sectors; update procurement so crypto-agility, key life-cycle management, and “harvest now, decrypt later” mitigation become baseline requirements; and adopt “cryptographic resilience” via agile standards, testing, and incident playbooks.

  2. Harmonize among allies: coordinate export controls, investment screening, and supply-chain security via mechanisms such as a proposed G7 Quantum Technology Point of Contact Group and narrowly scoped license-exception approaches in Five Eyes/AUKUS-style arrangements, while avoiding poorly designed measures that impose high compliance costs and chill benign collaboration.

  3. Incentivize global collaboration and capacity building: federate national quantum clouds, SDG-oriented demonstrators, and regional test networks under common governance rules; and consider, longer-term, a “CERN for Quantum” that provides shared access anchored in transparency and equitable access, including for Global South partners.

  4. Institutionalize foresight and bounded algorithmic regulation: resource international foresight capacities—within an IQA-type body or linked observatories—to update risk scenarios and stress-test legal frameworks, while experimenting with limited, well-governed AI-assisted monitoring and red-teaming to inform accountable human decision makers.

Takeaway for AIRecht’s readership

For legal and policy practitioners, the brief’s message is that quantum governance is entering a phase where operational artifacts—standards, benchmarks, procurement baselines, and interoperability profiles—will increasingly determine real-world rights, liabilities, and security outcomes. PQC migration and quantum networking are treated as the near-term proving ground for whether democracies can coordinate “security-sufficient openness” at scale.

For innovators and investors, the brief underscores that governance is not a brake on quantum progress but a design constraint that—if addressed early—can preserve global interoperability, reduce fragmentation, and support responsible diffusion of quantum capability without deepening geopolitical divides.

Meer lezen
War on the Rocks Publishes "A Bletchley Park for the Quantum Age"

Washington DC, Nov. 6, 2025—War on the Rocks has published a major new commentary by Stanford RQT’s Mauritz Kop, titled “A Bletchley Park for the Quantum Age.” The article translates his broader research on quantum governance into a concrete, operational blueprint for post-quantum cryptography (PQC) migration across the United States and its allies.

Appearing in a venue read closely by practitioners in defence, intelligence, and foreign policy, the piece draws a deliberate conceptual line from the World War II codebreaking effort at Bletchley Park to today’s challenge of securing democratic communications. It argues that Bletchley Park was more than a geographic location; it was a method—an integrated system of science, engineering, operations, and alliance management. Kop contends that a similar methodology is required now to protect national security systems against cryptanalytically relevant quantum computers.

The Enigma Machine utilized a complex series of electromechanical rotors to produce a polyalphabetic substitution cipher, creating an encryption standard that was widely deemed unbreakable by contemporary adversaries. Defeating this system required the Allies to operationalize abstract mathematics into industrial capability, a feat that fundamentally altered the trajectory of the war.

The article situates PQC migration not as a narrow information technology upgrade, but as a core tenet of United States and allied quantum-AI grand strategy. It highlights how flagship programmes such as the United States Department of Defense’s Replicator initiative must be made “quantum-ready” to avoid becoming silently obsolete once large-scale quantum computers arrive.

Professor Kop extends his gratitude to War on the Rocks editor Lieutenant Colonel Walter ‘Rick’ Landgraf, PhD, whose precise editorial work helped sharpen the argument and tailor it to the publication’s strategic readership.

The Core Argument: A Bletchley Method for Post-Quantum Cryptography Migration

The essay begins from a straightforward technical premise. Once fault-tolerant quantum computers exist, Shor’s algorithm will efficiently factor large integers and compute discrete logarithms, thereby breaking the public-key cryptosystems—such as RSA and elliptic-curve cryptography—on which secure communication currently relies. In parallel, Grover’s algorithm will provide a quadratic speed-up in brute-force search, effectively halving the security margin of many symmetric-key schemes.

In this setting, the world’s cryptographic infrastructure cannot simply be patched at the margins. It requires a comprehensive, carefully managed transition to new, quantum-resistant algorithms.

Kop proposes that the United States and its allies apply a “Bletchley method” to this problem by tightly linking:

  1. Domestic execution of PQC migration, and

  2. An allied, standards-based certification compact that prevents fragmentation.

Defensively, this means post-quantum cryptography by default and certified interoperability across critical systems. Politically, it means that Washington earns the right to lead abroad by delivering verifiable results at home.

The framework is organised around two distinct but mutually reinforcing tracks:

  • Track One – “Ultra at Home”: rigorous domestic execution, and

  • Track Two – “Allied Codebook Abroad”: international architecture designed to avoid a “quantum splinternet.”

Meer lezen
Music Law and Artificial Intelligence: From Cloned Artists to AI-Generated Works

The rise of artificial intelligence (AI) in the music industry is sparking a revolution, profoundly changing how music is created. This development raises complex legal questions concerning AI and copyright, including related rights. How can we protect the creative rights of artists and composers while simultaneously allowing room for technological innovation? In this comprehensive yet accessible legal overview, we explore key issues regarding AI and music. These include whether AI can legally train on copyrighted materials without consent, TDM exceptions, how various rights organizations (such as Buma/Stemra and Sena) approach AI, the status of AI-generated musical works, the threshold of human creativity required, protection against AI voice cloning via privacy laws and moral rights, contractual implications, new obligations under the EU AI Act, differences between European and American law, and ongoing lawsuits. This article is tailored for artists, composers, music publishers, labels, voice actors, producers, and AI companies seeking clarity on their legal standing.

AI Training on Protected Music and Video Materials: Legal Framework and Debate

Can an AI model in the Netherlands and the EU train on copyrighted material (such as music or video) without permission from the rights holders? Generally, using protected material beyond private use or citation requires permission. Scraping or using data for AI training without permission is typically considered infringement unless a specific legal exception applies.

Buma/Stemra’s Opt-Out Policy

In the Netherlands, Buma/Stemra explicitly uses its opt-out rights, requiring prior consent for TDM on its repertoire, thus ensuring fair compensation for composers and lyricists.

EU AI Act: Transparency Obligations and System Monitoring

The EU AI Act, effective from August 2025, introduces important transparency requirements, obliging generative AI model developers to:

  1. Disclose training data used, including copyrighted music or texts.

  2. Maintain policies ensuring compliance with EU copyright law.

  3. Respect explicit opt-out signals from rights holders during training.

The Act doesn't prohibit using protected material for training outright but enforces transparency and compliance through oversight and penalties.

Composition, Lyrics, and Master Recordings: Different Rights Regimes

Music rights in the Netherlands broadly split into:

A. Copyright: Protects compositions and lyrics, managed by organizations like Buma/Stemra.

B. Neighboring Rights: Protect recordings and performances, managed by Sena.

AI-Generated Compositions and Lyrics: Completely AI-generated works often fail to meet traditional copyright criteria, as human creativity is essential.

Neighboring Rights: It remains uncertain whether AI-generated performances and recordings attract neighboring rights, as these typically rely on human involvement.

Copyright Status of AI-Generated Music

In the U.S., fully AI-generated works explicitly do not receive copyright protection. While Europe hasn't clarified explicitly, the prevailing legal view aligns with this stance—AI-generated works likely fall into the public domain unless there's significant human creativity involved.

Hybrid Creations: Music combining human and AI input may qualify for copyright protection depending on the human creative contribution's significance.

AI Voice Cloning: Personality Rights and Privacy

AI voice cloning technology poses challenges regarding personal rights and privacy. Artists may invoke:

  1. Privacy rights under EU law (Article 8 ECHR).

  2. Personality rights.

  3. Potential trademark and image rights analogously.

The EU AI Act mandates transparency in AI-generated content, aiming to mitigate unauthorized use and deepfake concerns.

Music Contracts in the AI Era

Existing music contracts require updates addressing AI-specific matters, including (1) Explicit licensing terms for AI training; (2) Ownership clarity of AI-generated content; and (3) Liability assignment for copyright infringements involving AI.

Conclusion: Balancing Innovation and Rights—Be Prepared

The intersection of AI and music law presents both opportunities and challenges. Stakeholders should proactively:

  1. Clearly define rights in AI-generated music contractually and update existing music contracts.

  2. Specify permissions (licenses) and restrictions (opt-out) regarding AI training explicitly.

  3. Seek specialized music & AI legal advice to navigate evolving regulations.

By strategically addressing these issues, artists, companies, and AI developers can legally and effectively harness AI innovations, maintaining both creative and commercial control.

Meer lezen
Public Property from the Machine published in Harmonizing Intellectual Property Law for a Trans-Atlantic Knowledge Economy

Brill | Nijhoff's edited volume Harmonizing Intellectual Property Law for a Trans-Atlantic Knowledge Economy—edited by Péter Mezei, Hannibal Travis, and Anett Pogácsás, with a foreword by Maciej Szpunar—includes a chapter by Mauritz Kop, founder of the Stanford Center for Responsible Quantum Technology, titled Public Property from the Machine. The chapter confronts the question generative artificial intelligence forces on intellectual property law: who should own what a machine makes when no human authored it.

A new category, not a new right

Kop's answer breaks with the reflex to meet new output with new ownership. He argues that human authorship and inventorship remain the normative basis of copyright and patent law, and that—on the chapter's account—extending those rights to fully AI-generated works would chill innovation, narrow cultural diversity, and crowd the commons. In their place he proposes Res Publicae ex Machina—public property from the machine—a deliberately designed, permission-free public-domain regime for creations and inventions that have crossed the autonomy threshold, the point at which output is produced without meaningful human creative contribution. He frames the move as a Pareto improvement: many gain access, and no legal person loses a right that was ever warranted.

Rooted in the articulated public domain

The proposal develops Kop's earlier AI & Intellectual Property: Towards an Articulated Public Domain, published in the Texas Intellectual Property Law Journal in 2020, which argued for designing the public domain deliberately rather than treating it as the leftover of whatever rights fail to attach. The 2024 chapter applies that foundation to machine-generated subject matter under a named regime—so the two are best read as a sequence: the foundational article first, the autonomous-output application second. The same design-first instinct that animates Kop's responsible-innovation work, including the Ten Principles for Responsible Quantum Innovation, runs through the chapter: shape the rules before the defaults harden.

Why it matters for trans-Atlantic IP

Placing the argument inside a volume on trans-Atlantic harmonization is deliberate. The familiar questions—can an AI be an author, can an AI be an inventor—assume ownership is the only available category. Public Property from the Machine insists that public property is a category too—one the chapter argues is more defensible for output no human authored. For the United States and Europe, the practical question becomes not how to extend private rights to machines but what to agree to leave free. The fuller portrait of the scholar behind the proposal is set out in the Mauritz Kop profile. The chapter is a scholarly proposal rather than a statement of existing law—but it reframes a debate that has too often had only one answer on offer.

Meer lezen
Mauritz Kop and Mark Lemley Host High-Level EU Cybersecurity Delegation at Stanford Law

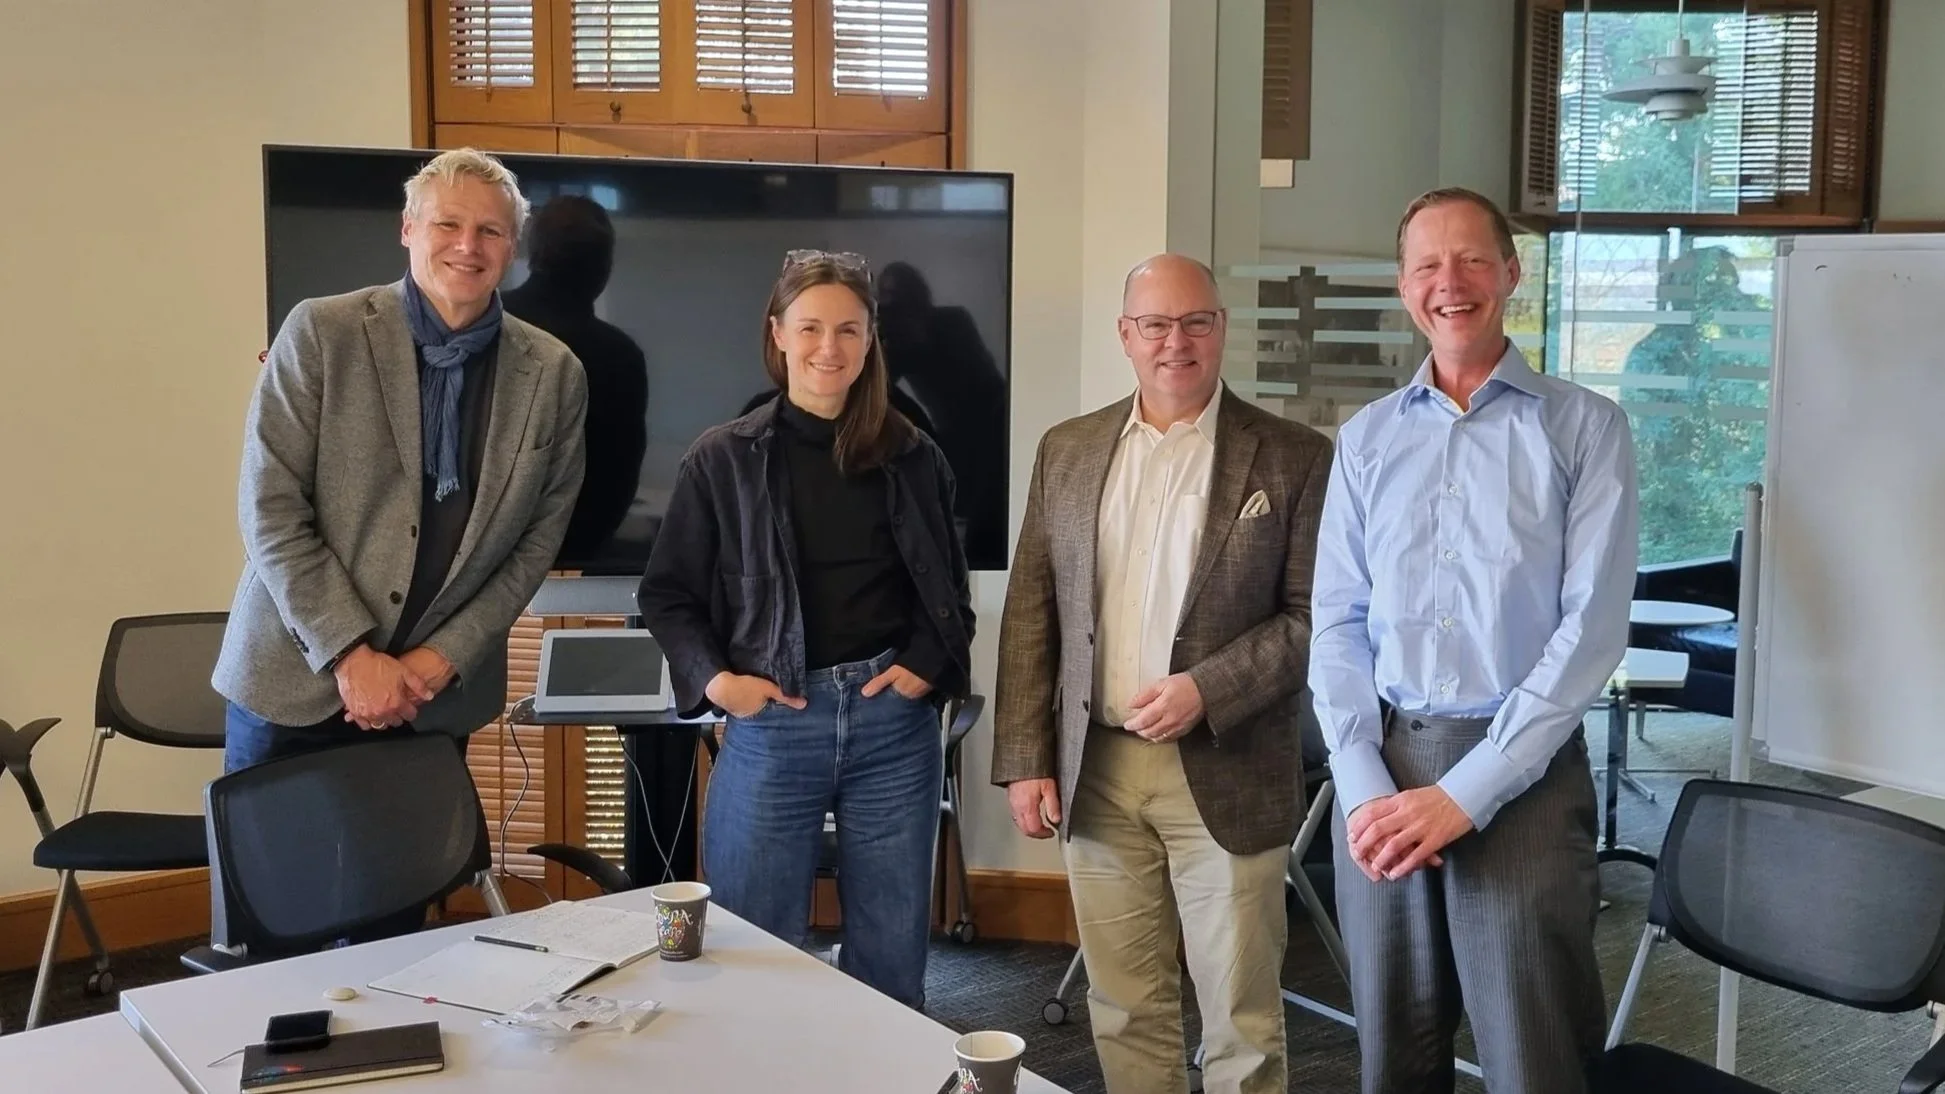
Stanford, CA – On February 26, 2024, the Stanford Center for Responsible Quantum Technology (RQT), a leading interdisciplinary hub operating under the aegis of the Stanford Program in Law, Science & Technology, had the distinct honor of hosting a high-level cybersecurity delegation from the European Commission. The meeting, led by the Center’s Founding Director, Mauritz Kop, and Professor Mark A. Lemley, Director of the Stanford Program in Law, Science & Technology, underscored the growing importance of transatlantic dialogue in shaping the future of digital security and responsible innovation in the quantum age.

The Stanford Center for RQT is dedicated to steering the development and application of quantum technologies toward outcomes that are not only innovative but also equitable, transparent, and beneficial for society at large. Its mission is to proactively address the complex ethical, legal, societal, policy and interoperability implications of quantum advancements, fostering a global ecosystem grounded in democratic values and human rights. The Center was officially inaugurated on December 6, 2023, by His Excellency Mark Rutte, then Prime Minister of the Netherlands and the current Secretary General of NATO, a testament to the geopolitical significance of its work. This recent meeting with the EU delegation builds on that foundation, reinforcing the Center’s role as a crucial bridge between Silicon Valley’s technological frontier and the world’s leading policymakers.

The dialogue centered on some of the most pressing challenges and opportunities at the intersection of quantum technology and cybersecurity, including building global capacity for responsible innovation and aligning EU and US national security strategies.

The EU Cybersecurity Delegation at Stanford RQT

The European Commission’s Cybersecurity Delegation was led by Gerard de Graaf, the Senior Envoy for Digital to the U.S. and Head of the European Union Office in San Francisco. A veteran of the European Commission with a distinguished career spanning several key digital policy areas, Mr. de Graaf is at the forefront of the EU’s efforts to promote a human-centric, ethical, and secure digital transition. His role involves strengthening transatlantic cooperation on digital regulation, from data governance and AI to cybersecurity and platform accountability. Mr. de Graaf, who was also present at the Center’s inauguration, has been a pivotal figure in shaping the EU’s landmark digital policies, including the General Data Protection Regulation (GDPR) and the Digital Services Act (DSA). His leadership in the San Francisco office is instrumental in fostering dialogue between European regulators and the heart of the global tech industry.

Accompanying Mr. de Graaf were Joanna Smolinska, Deputy Head of the EU Office in San Francisco and a key figure in transatlantic tech diplomacy, and Ilse Rooze, a Seconded National Expert at the EU Office who brings deep expertise in digital policy and international relations.

Representing Stanford were Mauritz Kop and Professor Mark A. Lemley. Mr. Kop is a pioneering scholar in the governance of emerging technologies, with a focus on quantum, AI, and intellectual property. As the Founding Director of the RQT Center, his work is dedicated to creating robust legal and ethical frameworks to ensure that transformative technologies are developed and deployed responsibly. Professor Lemley is the William H. Neukom Professor of Law at Stanford Law School and one of the world's most cited scholars in intellectual property and technology law. His extensive work on innovation, competition, and the digital economy provides a critical legal and economic lens through which to view the challenges of the quantum era.

The Quantum Cybersecurity Challenge: Preparing for Q-Day

A central theme of the discussion was the looming threat that fault-tolerant quantum computers pose to global cybersecurity. The immense processing power of these future machines will render much of the world’s current cryptographic infrastructure obsolete. This critical juncture, often referred to as “Q-Day” or the “Quantum Apocalypse,” is the moment when a quantum computer will be capable of breaking widely used encryption standards like RSA and ECC, which protect everything from financial transactions and government communications to personal data and critical infrastructure.

The implications of Q-Day are profound. Malicious actors could potentially decrypt vast archives of stolen encrypted data—a scenario known as "harvest now, decrypt later." This retroactive decryption capability poses a severe threat to long-term data security, national security, and economic stability.

In his opening remarks, Mauritz Kop emphasized the urgency of a proactive, coordinated global response. The conversation explored the transition to Post-Quantum Cryptography (PQC), a new generation of cryptographic algorithms designed to be resistant to attacks from both classical and quantum computers. The U.S. National Institute of Standards and Technology (NIST) is in the final stages of standardizing a suite of PQC algorithms, a process closely watched by governments and industries worldwide. The delegation discussed the immense logistical, technical, and financial challenges of migrating global IT systems to these new technical standards—a process that is expected to take more than a decade and require unprecedented public-private collaboration.

The discussion also touched upon other quantum security technologies, such as Quantum Key Distribution (QKD), which uses the principles of quantum mechanics to create secure communication channels. While PQC focuses on developing new mathematical problems that are hard for quantum computers to solve, QKD offers a physics-based approach to security. The participants explored how these different technologies could complement each other in a future-proof security architecture.

Meer lezen